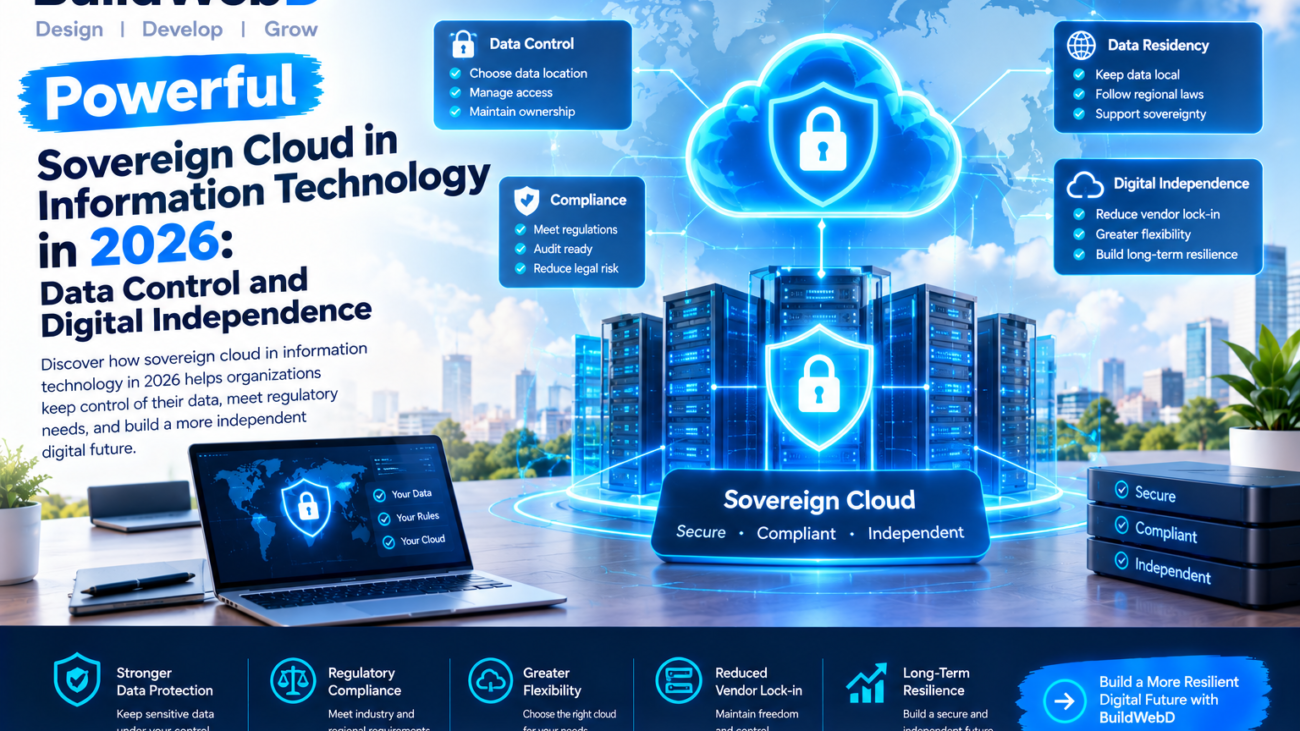
sovereign cloud in information technology in 2026

Powerful Sovereign Cloud in Information Technology in 2026: Data Control and Digital Independence

Cloud computing has transformed how businesses store information, run applications, and deliver digital services. Organizations can scale their infrastructure without maintaining every server themselves. However, as more critical operations move to the cloud, businesses are asking an important question: who controls their data, where is it stored, and which laws govern it?

These questions are driving interest in sovereign cloud in information technology in 2026. This approach focuses on giving organizations greater control over data, infrastructure, and cloud operations according to specific legal, regulatory, and business requirements.

For governments, financial institutions, healthcare providers, and companies handling sensitive information, sovereign cloud is becoming an important consideration in long-term IT planning.

What Is a Sovereign Cloud?

A sovereign cloud is a cloud environment designed to support digital sovereignty requirements. Depending on the provider and deployment model, these requirements may include controlling where data resides, who can access it, how services are operated, and which jurisdiction’s laws apply.

Traditional cloud services often emphasize scalability, flexibility, and global availability. Sovereign cloud adds another layer of consideration: the organization’s ability to exercise appropriate control over its digital assets.

It is important to understand that data residency and data sovereignty are not identical. Data residency refers primarily to where information is stored or processed. Data sovereignty includes broader questions about legal jurisdiction, operational authority, access, and control.

A cloud service that stores data in a particular country does not automatically satisfy every sovereignty requirement. Organizations need to evaluate the provider’s legal structure, operational arrangements, technical safeguards, and contractual commitments.

Why Sovereign Cloud Matters in 2026

Digital services now support essential business activities, from payments and customer management to artificial intelligence and public administration. Losing control over critical data or becoming unable to access important systems can create operational, financial, and regulatory risks.

Interest in sovereign cloud in information technology in 2026 is growing as organizations reassess cloud dependency, jurisdictional exposure, and resilience.

Gartner forecasts worldwide sovereign cloud infrastructure-as-a-service spending of approximately $80 billion in 2026, representing 35.6% growth over 2025. This signals increasing investment in cloud environments designed to meet sovereignty requirements. <Cite refs={[“turn905360search0”]} />

For businesses, the implications extend beyond data storage. Cloud decisions can influence vendor risk, disaster recovery, AI deployment, regulatory planning, and the ability to change providers in the future.

How Does Sovereign Cloud Work?

Sovereign cloud is not one single technology. It is a combination of infrastructure, policies, technical controls, contracts, and operational practices.

Data location controls: Organizations can select cloud regions and configurations that help keep specific data within approved geographic boundaries.

Access management: Identity controls, privileged-access restrictions, logging, and approval processes help define who can manage systems or access sensitive information.

Encryption and key control: Encryption protects data, while carefully managed cryptographic keys can provide additional control over who can decrypt it. The precise arrangement depends on the service and its design.

Operational governance: Organizations may require local operational oversight, defined support arrangements, auditability, or restrictions on administrator access.

Compliance monitoring: Policies and monitoring tools can help enforce approved configurations and identify changes that conflict with organizational requirements.

When evaluating sovereign cloud in information technology in 2026, businesses should examine these controls together rather than relying on a provider’s marketing label alone.

Key Benefits for Businesses

1. Greater Data Control

Sovereignty-focused cloud arrangements can help businesses define where sensitive information is stored and which people or systems may access it. This is especially relevant when handling confidential customer, financial, or government data.

2. Support for Regulatory Requirements

Organizations operating in regulated industries may need to demonstrate compliance with data protection, sector-specific, or geographic requirements. A suitable cloud arrangement can support those obligations, although the cloud service alone does not guarantee compliance.

3. Stronger Risk Management

Understanding where data resides and how providers operate can help organizations identify legal, operational, and vendor-related risks before they affect business continuity.

4. Greater Strategic Flexibility

A carefully designed cloud architecture can reduce unnecessary dependence on a single provider. Portable applications, documented data-export procedures, and open standards may make future transitions easier.

5. More Confidence for Sensitive Workloads

Organizations may be more comfortable moving selected workloads to cloud environments when the provider can demonstrate appropriate controls over data, access, and operations.

Who Should Consider Sovereign Cloud?

Government agencies may need cloud environments aligned with national security, public-sector procurement, and public data requirements.

Financial institutions can evaluate sovereignty controls when processing sensitive financial information or supporting regulated operations. Healthcare organizations may consider them for systems that handle patient information, subject to applicable laws and security requirements.

Businesses using AI may also need to examine where training data, prompts, model outputs, and related records are processed. A sovereignty-focused cloud arrangement can be part of the solution, but AI governance and model security require additional controls.

Not every organization needs a dedicated sovereign cloud. The appropriate approach depends on the sensitivity of the data, regulatory obligations, risk tolerance, and available budget.

Challenges and Limitations

Sovereign cloud can introduce higher costs, fewer service choices, or additional operational complexity compared with some standard cloud configurations. Specialized services may not be available in every region, and geographic restrictions can affect performance or resilience planning.

Another challenge is understanding what a provider’s sovereignty claims actually cover. Data location alone may not address foreign legal access, software supply-chain dependencies, support access, or control over encryption keys.

Organizations should also avoid assuming that local infrastructure is automatically more secure. Security still depends on sound architecture, identity management, patching, monitoring, incident response, and reliable backup procedures.

How to Prepare Your IT Strategy

Start by classifying your data and identifying the systems that face the strictest legal or business requirements. Map where information is stored, processed, backed up, and accessed by third parties.

Next, define the controls your organization needs. These may include geographic restrictions, customer-managed keys, local operational oversight, audit logs, recovery arrangements, and clear contractual commitments.

Compare providers against documented requirements instead of relying only on product names. Test recovery procedures, assess service portability, and review the cost of meeting sovereignty requirements over time.

Finally, maintain a balanced architecture. Use sovereignty-focused controls where they address real risks, while selecting other cloud models for workloads that do not require the same level of restriction.

Conclusion

Sovereign cloud in information technology in 2026 reflects a broader shift toward treating data control and digital independence as strategic IT priorities. By evaluating data location, jurisdiction, operational access, encryption, and vendor dependency, organizations can make more informed cloud decisions.

The best approach is not automatically to move every workload into a sovereign environment. It is to identify genuine requirements, compare providers carefully, and build a cloud strategy that balances control, resilience, cost, and innovation.

At BuildWebD, we believe successful digital transformation starts with thoughtful technology decisions. Whether you are developing business applications, modernizing IT systems, or planning secure cloud-based services, a clear strategy can help you build a more resilient digital future.

Ready to strengthen your digital foundation? Connect with BuildWebD to plan practical, reliable technology solutions for your business.
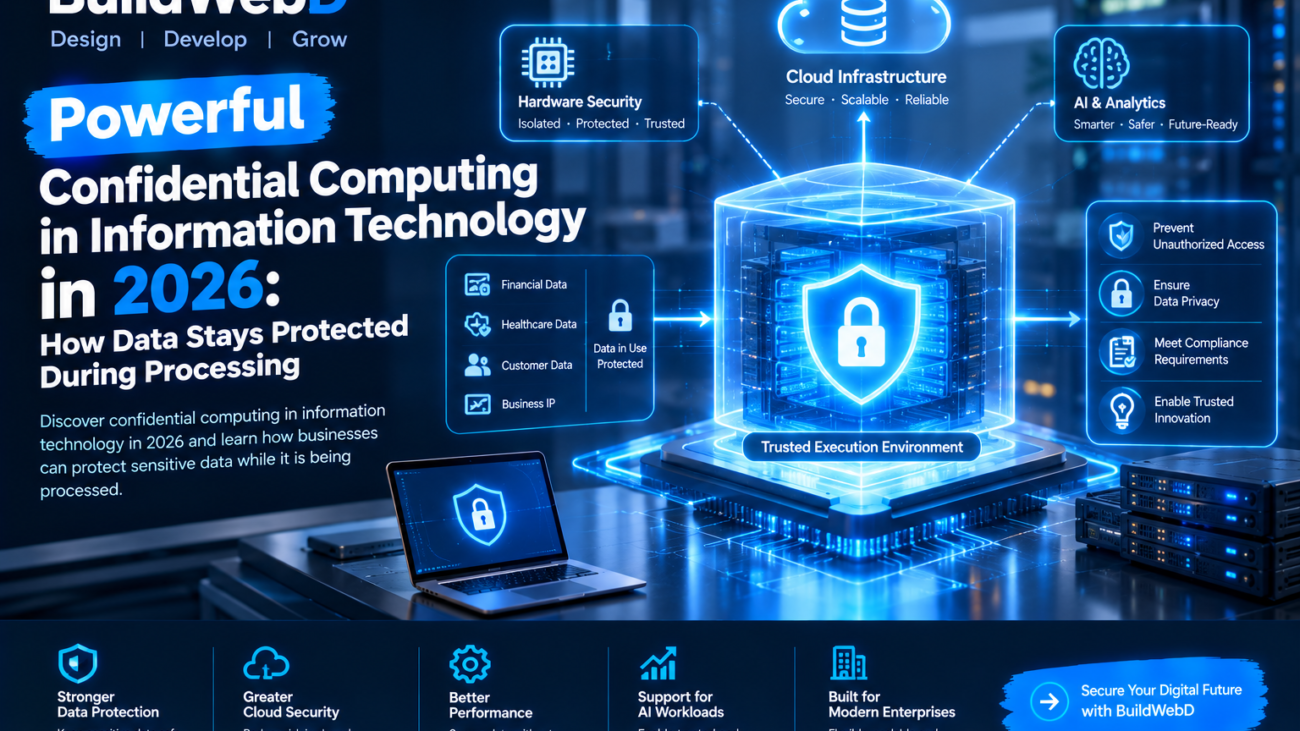
confidential computing in information technology in 2026

Powerful Confidential Computing in Information Technology in 2026: How Data Stays Protected During Processing

Businesses rely on cloud platforms, artificial intelligence, digital payments, and connected applications to manage sensitive information. However, protecting data while it is stored or transferred is only part of the cybersecurity challenge. Information must also remain secure while applications actively process it.

This is where confidential computing in information technology in 2026 becomes increasingly important. This approach helps protect sensitive information during processing by isolating workloads inside hardware-based trusted execution environments. It gives organizations another layer of security as they modernize their digital infrastructure.

From financial services to healthcare and enterprise AI, confidential computing can help businesses strengthen privacy, improve trust, and reduce certain risks associated with processing sensitive data.

What Is Confidential Computing?

Confidential computing is a security approach designed to protect data while it is being processed. Traditional security measures commonly focus on data at rest, such as files stored on a server, and data in transit, such as information moving between an application and a cloud service.

Data in use presents a different challenge because applications must access information to perform calculations, generate results, or execute transactions.

Confidential computing addresses this challenge through trusted execution environments (TEEs). These hardware-supported environments isolate selected workloads and help prevent unauthorized access to their contents, including from certain privileged software or infrastructure layers.

The exact protection depends on the processor, platform design, configuration, and threat model. It is not a replacement for encryption, access controls, or secure application development. Instead, it adds another security layer to a broader protection strategy.

Why Confidential Computing Matters in 2026

As organizations adopt AI tools and move more workloads to cloud platforms, they increasingly need to process information that cannot be exposed unnecessarily. This includes financial records, customer details, business strategies, proprietary datasets, and confidential research.

Confidential computing in information technology in 2026 matters because it helps organizations address the security gap that can exist while sensitive data is actively being used.

For example, a company may need to analyze customer information through a cloud-based service without giving the cloud infrastructure unnecessary access to the underlying data. A suitable confidential computing deployment can help reduce exposure during that processing.

The approach is also relevant to AI workloads. Organizations may want to use sensitive business data with AI models while strengthening safeguards around the processing environment. As Gartner identifies confidential computing as a strategic technology trend, it deserves attention during infrastructure and security planning.

How Does Confidential Computing Work?

Confidential computing generally combines specialized hardware capabilities, trusted execution environments, and verification mechanisms.

First, a supported processor establishes an isolated execution area. An application or selected workload runs within this protected environment, separating its sensitive operations from other parts of the system.

Second, hardware-backed protections help restrict unauthorized access to the workload’s memory and execution state. Depending on the platform, these controls can reduce exposure to the host operating system, hypervisor, or other privileged components.

Third, remote attestation may allow a separate system to verify that a workload is running in an expected, trusted environment before releasing sensitive data or credentials. The verification process and security guarantees vary by implementation.

Finally, applications continue performing their normal tasks while the protected environment provides additional safeguards.

This is the core idea behind confidential computing in information technology in 2026: protect information not only when it is stored or transferred, but also while it is being processed.

Key Benefits for Modern Businesses

1. Stronger Data Privacy

Organizations can use confidential computing to limit exposure of sensitive information during processing. This is especially useful when workloads run on shared or externally managed infrastructure.

2. More Secure Cloud Workloads

Cloud computing provides flexibility, but businesses may have concerns about privileged access and infrastructure trust. Confidential computing can help reduce specific risks by isolating supported workloads.

3. Better Protection for AI Workloads

AI systems may process proprietary documents, customer records, or confidential datasets. Suitable confidential computing environments can add safeguards around certain data-processing operations, although they do not automatically prevent model-level leaks or insecure application behavior.

4. Improved Collaboration

Different organizations sometimes need to analyze shared information without broadly exposing their individual datasets. With appropriate architecture and governance, confidential computing can support more controlled collaboration.

5. Support for Security and Compliance Goals

Businesses handling regulated information can evaluate confidential computing as part of their broader security controls. However, using it does not automatically guarantee compliance with any specific law or industry standard.

Where Is Confidential Computing Used?

Confidential computing in information technology in 2026 has potential applications across several industries.

Banking and financial services: Financial institutions can explore protected environments for fraud analysis, risk calculations, and sensitive transaction processing.

Healthcare: Healthcare organizations may use suitable confidential environments when processing sensitive medical information, subject to applicable privacy requirements and system safeguards.

Artificial intelligence: Businesses can evaluate protected execution for selected AI inference and data-processing workloads involving confidential information.

Cloud services: Cloud providers and customers can use supported confidential virtual machines or containers to strengthen workload isolation.

Research and analytics: Organizations can investigate secure ways to collaborate on sensitive datasets while limiting unnecessary exposure.

The suitability of each use case depends on the technology, performance requirements, legal obligations, and the security threats the organization needs to address.

Challenges Businesses Should Consider

Despite its advantages, confidential computing is not a complete cybersecurity solution.

Compatibility is one challenge. Applications may require architectural changes or specific hardware and cloud services before they can use confidential environments effectively.

Performance is another consideration. Security features, memory limitations, and workload design can affect application speed and operating costs. Businesses should benchmark real workloads before making deployment decisions.

Key management and attestation also require careful planning. Teams must determine who can approve workloads, how credentials are released, and what happens if a system fails verification.

Most importantly, confidential computing cannot eliminate vulnerabilities inside an application. Weak authentication, malicious code, excessive permissions, insecure APIs, and poor data handling can still create security risks.

Before deploying confidential computing in information technology in 2026, businesses should define their threat model, assess platform capabilities, test performance, and establish monitoring and incident-response procedures.

How to Prepare Your IT Infrastructure

Start by identifying applications that process highly sensitive information. These may include customer databases, financial workloads, AI applications, or proprietary business systems.

Next, consult your cloud provider or hardware vendor to determine which confidential computing capabilities are available. Review the isolation model, attestation options, supported workloads, key management, and limitations.

Run a small pilot before migrating critical systems. Measure performance, test failure scenarios, and verify that the application behaves correctly inside the protected environment.

Finally, combine confidential computing with established security practices, including encryption, identity management, least-privilege access, secure coding, vulnerability testing, and regular audits.

A phased approach helps organizations understand the benefits and limitations before committing to a wider rollout.

The Future of Confidential Computing

As AI adoption and cloud-based operations continue to expand, protecting data during processing will remain an important part of security architecture. Confidential computing may become particularly valuable for organizations that need stronger trust boundaries around sensitive workloads.

Future developments will depend on hardware improvements, easier deployment tools, wider platform support, and clearer verification processes. Businesses should follow these developments without assuming that every workload requires confidential computing.

The strongest strategy is to select security controls according to the sensitivity of the data, the operating environment, and the consequences of unauthorized access.

Conclusion

Confidential computing in information technology in 2026 offers organizations an additional way to protect sensitive data while applications process it. By combining trusted execution environments, hardware-backed isolation, and verification mechanisms, businesses can strengthen security across selected cloud, analytics, and AI workloads.

However, successful adoption requires more than enabling a hardware feature. Organizations must evaluate their risks, choose compatible platforms, manage access carefully, and maintain strong application security practices.

At BuildWebD, we believe modern digital solutions should be designed with performance, reliability, and security in mind. Whether you are upgrading business applications or planning a more secure digital infrastructure, the right technology strategy can help your organization prepare for the future.